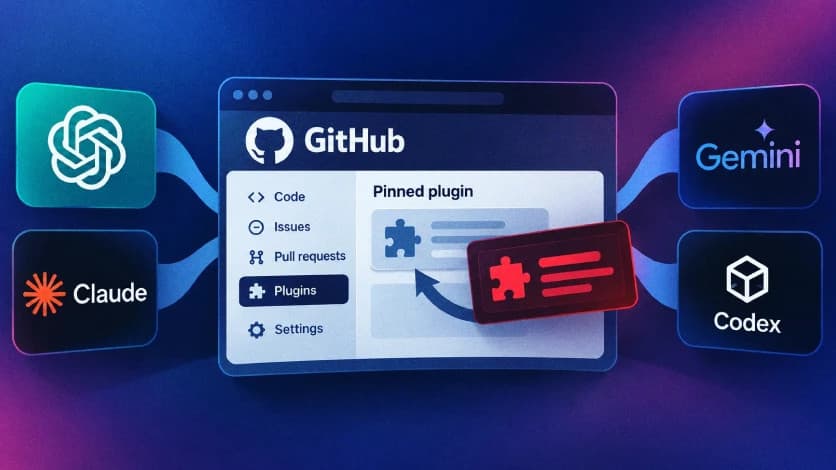
Plugin4Shell, a zero-click vulnerability disclosed on September 17–18, lets whoever controls an AI coding agent's plugin repository silently replace approved plugin code with malicious code — and as of this week, two of the four affected tools still have no fix. Anthropic's Claude Code and OpenAI's Codex have shipped patches; GitHub Copilot has not, and Google is retiring Gemini CLI rather than fixing it, WION reported on September 20.
The flaw was found by researchers at AIR Security, who reported it to the four vendors in June 2026 before going public, according to The Hacker News. It is being described as the first true supply-chain vulnerability in the AI agent ecosystem. No CVE identifier (the standard catalog number for security flaws) had been assigned at disclosure.
How the SHA-pinning bypass works
AI coding agents let users install plugins, and they lock each installed plugin to a specific, reviewed version using its Git commit hash — a fingerprint called a SHA pin. Plugin4Shell defeats that lock with a Git quirk: an attacker who controls the plugin's repository creates a branch whose name looks exactly like the pinned 40-character commit hash. When the agent fetches the "pinned" version, Git resolves the hash-shaped branch name instead of the real commit — delivering the attacker's code while the agent still reports the correct, approved version number.
Because agents auto-update plugins in the background — the default behavior in Claude Code and Codex — the swap needs no click, no prompt and no approval from the user. A compromised plugin then runs with the developer's full access: source code, saved credentials and any system the machine can reach.
One important limit: GitHub itself blocks branch and tag names shaped like commit hashes, so plugins hosted on GitHub are protected. The attack works against plugins hosted on Bitbucket, private Git servers and other non-GitHub hosts.
Patch status at a glance
| Agent | Vendor | Status | What to do |
|---|
| Claude Code | Anthropic | Fixed in version 2.1.179 | Update now |
| Codex | OpenAI | Fixed in version 0.146.0 | Update now |
| GitHub Copilot | Microsoft/GitHub | No fix available | Audit plugins, limit non-GitHub sources |
| Gemini CLI | Google | No fix — tool being retired | Migrate to Antigravity |
What this means for Filipino developers
There is no Philippine-specific advisory on Plugin4Shell, but the exposure here is real because these tools are in real local use. Anthropic's own usage data, published in August, put software development at 16.63% of Filipino Claude requests — the country's second-largest use case — with Metro Manila, CALABARZON and Central Visayas together accounting for about 74% of local activity. Those are the same corridors where the country's IT-BPM and software teams sit, and GitHub Copilot — the tool still without a fix — is one of the most widely adopted coding assistants in workplaces generally. Claude's growing footprint in Philippine enterprises, including Salesforce's Claude-powered push and its new AI hub in BGC, makes the patched-versus-unpatched split worth checking on every team machine.
The practical checklist is short:
- Update Claude Code to at least 2.1.179 and Codex to at least 0.146.0.
- On Copilot and any still-unpatched agent, review installed plugins and treat anything hosted outside GitHub as suspect until a fix ships.
- Consider disabling background plugin auto-updates where your agent allows it.
- Teams on Gemini CLI should plan the migration Google is pointing them to, since no patch is coming.
With the technical details now public and market-leading Copilot still exposed, the gap between disclosure and a fix is the risk worth acting on now.